Elephant Firewall supersedes the previous security blocking system, by adding two extremely fast layers running at Application Server scope.
The main advantages over the previous system are:
- Container-wide vs app-wide, preventing malicious attacks before they get into the application.
- Two layers vs one layer, it tracks IP and sub-net until either of them is punished, or expires. Then shifts to the blocking layer.
- Auto expire vs positive tracking, takes the burden out of the tracking system with a much lighter blocking layer.
- Small footprint, less use of memory and processing.
Monitoring server usage
| Main issues | Description |
|---|---|
| Volumetric DoS or rate-limit violation |
Low footprint requests with the purpose of exhausting application server resources. Checks upper and lower usage and applies a block when exceeded, based on lapsed-time. |
| Application server access violation |
Attempts to get access to server security. These actions are already protected by the app, the block prevents future attempts. Allows a minimum error margin and applies a block when exceeded, based on lapsed-time. |
| Excessive usage of obfuscation |
Thorough readings of app resources, using time-restricted calls. Checks upper and lower usage and applies a block when exceeded, based on lapsed-time. |
| Automated resource-scrapers |
Resource scrapers with no real intention. Checks upper and lower usage and applies a block when exceeded, based on lapsed-time. |
| Unregistered or aggressive crawler subnet |
Aggressive calls through sub-nets. Checks upper and lower usage and applies a block when exceeded, based on lapsed-time. |
White-listing
Elephant Firewall recognizes in-app work actions, allowing visitors to have a big load of working data.
Status
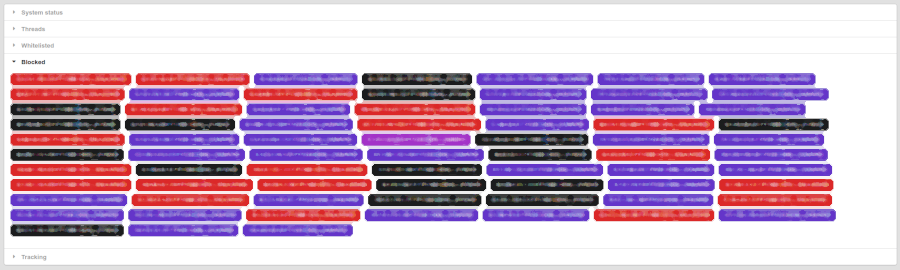
Firewall status is included in BaaS Console -> Tools -> Settings -> System Status.
Provides a view of current status, with whitelisted and blocked IPs (blurred in the example).